The Promise and the Trap of Enrichment
Data enrichment is one of the most powerful tools in a detection engineer's kit. It is also one of the most misused. Enrichment can turn a bare alert into something an analyst can act on more quickly, but it cannot turn a weak detection into a strong one.
I see the same pattern over and over. A team buys a threat intel feed, wires it into the SIEM, and expects their detection program to level up overnight. What they get instead is a flood of IOC matches, a pile of low-value alerts with more fields attached, and analysts who are now spending more time reading context than acting on it.
One of my favorite examples of this is lovingly known as “The pew-pew map”. This is essentially a map that shows Geo-IP locations of blocked traffic where the IP matches a known threat actor from a threat intel feed. Now I will say, the pew-pew maps do tend to look very cool, and the companion metric of “Blocked attacks” is usually fairly impressive, but ultimately both are vanity metrics. None of the information in the pew-pew map nor the blocked attacks count are actionable. It usually goes up on a TV in the SOC and is great to show off to customers but that’s where the value ends.
The problem is not enrichment itself. The problem is order of operations. Enrichment amplifies whatever you already have. If your detections are well built and aligned to real threats, enrichment makes them sharper. If they are not, enrichment just makes the noise louder.
What Enrichment Actually Does
Enrichment adds context to an event or alert that the raw log does not carry on its own. It answers the questions an analyst would otherwise have to go look up: Who is this user? What is this host? Is this IP known? Does this asset matter?
That context can be used in two places:
- At triage time, where it saves the analyst lookups and speeds up the decision to escalate or close
- Inside the detection logic itself, where it changes whether a rule fires, how it is scored, or what severity it carries
What enrichment does not do is detect anything on its own. It does not tell you which behaviors matter in your environment. It does not fix a rule that is looking at the wrong data source or the wrong technique. It describes the alert. The rule still has to find the right thing in the first place.
Start With Your Threat Profile
Before you decide what to enrich, you need to know what you are defending against. Your threat profile is the set of adversaries, techniques, and scenarios that realistically apply to your organization based on your industry, your technology stack, your exposure, and your crown jewels.
A healthcare provider worried about ransomware and credential abuse needs different context than a SaaS company worried about cloud control plane abuse and API key leakage. The enrichment that matters most is the enrichment that answers questions your threat profile raises.
A few questions worth answering before you build anything:
- Which ATT&CK techniques are most relevant to the threats you actually face?
- Which of your detections cover those techniques today?
- When those detections fire, what does an analyst need to know to make a fast, correct decision?
- Where are analysts losing time pivoting to other tools for that answer?
The answers to that last question is your enrichment backlog.
Solid Rules Come First
Enrichment sits on top of your detections, so it inherits their flaws. If a rule is too broad, enrichment attaches context to thousands of irrelevant events. If a rule is tuned against the wrong field, or the log source behind it has silently stopped sending data, enrichment has nothing useful to decorate.
Before investing in enrichment, your rules should meet a basic bar:
- They map to techniques in your threat profile, not just techniques that were easy to write for
- They are tuned well enough that analysts trust them when they fire
- The data sources they depend on are healthy and parsed correctly
- Someone owns them and reviews them on a regular cadence
Once that foundation is in place, enrichment becomes a multiplier instead of a band-aid. A well-scoped rule with the right context attached is the difference between an analyst closing an alert in two minutes and spending twenty minutes reconstructing the story.
Enrichment Is Not Just Threat Intel
When most people hear "enrichment," they think of threat intel feeds: IP reputation, domain age, known bad hashes. Those have their place, but some of the most valuable enrichment I have built had nothing to do with external intel. It came from data the organization already owned.
Tying Identities Together
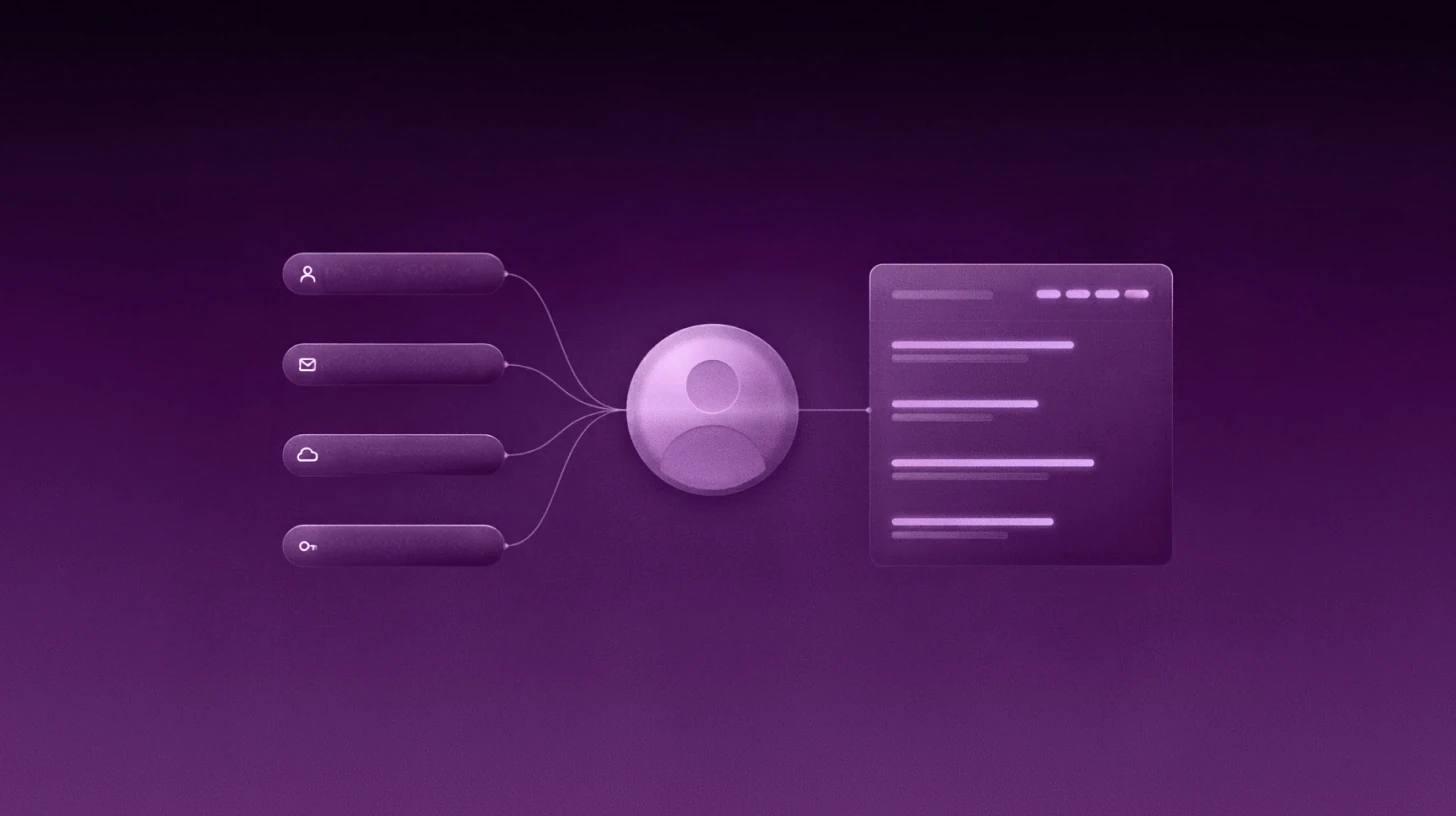
In some environments, a single person shows up under several identities. There is the Active Directory account, the UPN, the email address, the cloud IAM principal, the SaaS username, and sometimes a separate admin account. Each log source records whichever one it knows about.
Without enrichment, a rule looking for suspicious behavior by one user only sees a fraction of what that user is doing. Correlation across sources breaks, and analysts are left manually matching jdoe, john.doe@company.com, and DOMAIN\adm-jdoe.
I’ve personally built enrichments that map those account formats back to a single user entity. Once every event carries a common identity, rules can correlate behavior across sources, risk can accumulate against a real person instead of a string, and analysts see the whole picture in one place. Small changes like this that save a few seconds during a single investigation can compound exponentially over the course of a year.
Using Vulnerability Scanner Data to Inform Severity
Not every alert on every host deserves the same severity. An exploitation attempt against a server that is fully patched for that vulnerability is interesting. The same attempt against a server your scanner flagged as vulnerable last week is urgent.
I have also built enrichment that pulls vulnerability scanner findings into detection rules so the severity of an alert reflects the actual exposure of the target. That context can raise severity when the asset is known to be vulnerable, lower it when it is not, and give the analyst the CVE and asset details right in the alert.
The result is prioritization grounded in your environment rather than a static severity someone picked when the rule was written.
Other Internal Sources Worth Considering
- Asset inventory and CMDB data for business criticality and ownership
- HR data for role, department, and employment status
- Known admin and service account lists
- Approved software and change management records
Building Enrichment That Earns Its Keep
Enrichment has a cost. Lookups add latency and compute, feeds need maintenance, and every extra field on an alert is something an analyst has to read. A few principles keep that cost worth paying:
- Tie every enrichment to a question. If you cannot name the analyst question it answers or the rule decision it changes, it is clutter.
- Prefer enrichment that changes outcomes. Context that adjusts severity, suppresses known-good activity, or enables correlation is worth more than context that only displays.
- Treat enrichment sources like log sources. Lookup tables go stale, scanner exports stop running, and identity mappings drift as people join and leave. Monitor them the same way you monitor your data feeds.
- Measure the impact. Track triage time, escalation accuracy, and false positive rates before and after. If nothing moved, revisit the enrichment.
- Start small. Enrich the handful of high-value detections tied to your top threats first, prove the value, then expand.
Context Is a Multiplier, Not a Foundation
Enrichment is at its best when it amplifies detections that are already doing the right job. Know your threat profile, build and maintain rules that reflect it, and then add the context that helps those rules and your analysts make better decisions. Look inward as well as outward: some of your most valuable enrichment sources are already sitting in your identity systems, asset inventory, and vulnerability scanner.
At Rilevera, we help teams understand how their detections map to the threats that matter to them and keep an eye on the health of the rules and data sources those detections depend on. That foundation is what makes enrichment worth building. If you are thinking about where enrichment fits in your program, we are always happy to talk it through.